
How TrueNorth Protects Municipal Data in Canada
Protecting civic infrastructure with northamerica-northeast1 residency, Assured Workloads policy enforcement, and encryption at rest with Customer-Managed Encryption Keys (CMEK).
Trusted Compliance Standards
Our Ethical Commitment
Beyond compliance, TrueNorth is built on ethical AI principles that put municipalities in control. We believe AI should serve public servants, not the other way around.
Transparency
Every AI decision can be explained. We show our work with full source citations.
Human Oversight
Critical decisions always involve human judgment. AI assists, humans decide.
Fairness
We regularly audit for bias in zoning, bylaw, and municipal contexts.
Accountability
Clear escalation paths when AI makes mistakes. You're never left hanging.
Data Control
You can delete everything, anytime. No retention beyond your control.
Incident response commitment
Confirmed privacy or security incidents affecting your data are reported to your designated contact without undue delay, with containment steps and recommended actions (FOIPPA-aligned). Read our incident notification commitment →
Defense-in-Depth Architecture
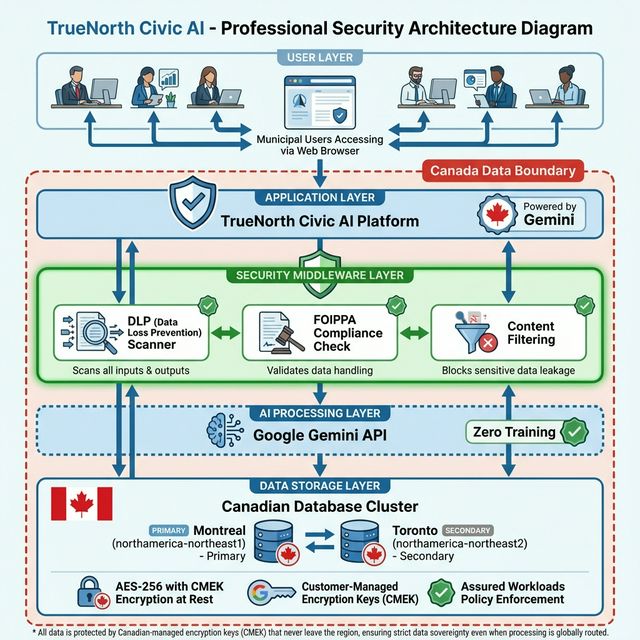
Our platform runs inside the Google Cloud "Canada Data Boundary", so documents and databases are stored only on servers in Canada and every transmission uses the strongest encryption available at each layer.
Technical Residency
Primary infrastructure is hard-pinned to northamerica-northeast1 (Montreal), with database and document storage encrypted using Canadian-managed keys (CMEK) that never leave the region.
Policy Enforcement
We use GCP Assured Workloads to apply organization-level policy constraints. They automatically block the creation of any resources (VMs, Buckets, DBs) outside approved Canadian regions.
Encryption at Rest
All data is encrypted at rest with Customer-Managed Encryption Keys (CMEK) and AES-256. The keys live in Google Cloud KMS inside the Canadian region, not in a foreign jurisdiction.
Canada Data Boundary
Part of our Assured Workloads control package, strictly enforcing the Canada Data Boundary. This includes restricting primary storage resources to Canadian regions and enforcing minimum TLS versions for all transit.
DLP Privacy Middleware
Every prompt is intercepted by our Cloud DLP API before reaching the AI model. We use Canadian-specific inspection templates to detect and redact sensitive data.
Canadian Identifiers
General PII
Security Architecture Overview
A comprehensive view of our defense-in-depth approach, showing how data flows through Canadian infrastructure with DLP scanning and FOIPPA compliance at every layer.
Hosted Exclusively in Canada
We store data in Google Cloud Platform's Montreal region (northamerica-northeast1) and protect it with customer-managed encryption keys (CMEK). We disclose that Google LLC is a US-headquartered company and residual US CLOUD Act jurisdiction exists. We mitigate this through contractual controls, encryption, and minimal data retention.
Primary: northamerica-northeast1
Montreal based low-latency clusters.
Failover: northamerica-northeast2
Toronto based disaster recovery.
Jurisdictional Control
Decryption keys managed separately from data.
Canadian Hosting Architecture
Montreal Server Node
Primary Cluster · northamerica-northeast1
Toronto Server Node
Standby Failover · northamerica-northeast2
Frequently Asked Questions
How do you mitigate the US CLOUD Act?
Like all platforms using US-headquartered cloud infrastructure, residual US CLOUD Act jurisdiction exists. We mitigate this through contractual controls with Google, encryption at rest (CMEK) and in transit, minimal 30-day auto-purge retention periods, and regular compliance audits. For municipalities requiring additional jurisdictional control, contact us to discuss options including Canadian-owned cloud providers.
How is municipal data isolated?
We use strict logical tenant isolation within our database clusters. Every query is scoped to a specific Tenant ID, ensuring that cross-contamination of municipal records is impossible at the database level.
Do you conduct penetration testing?
Yes. We engage independent third-party security firms to conduct penetration testing on our application and infrastructure twice annually. Summarized reports are available to enterprise customers upon request.
How are project documents protected?
Project documents are isolated by user, scanned by Cloud DLP before ingestion, and stored in Canadian-only GCP regions. Access is controlled at the project level within your specialized task workspace, ensuring that your research and data remain secure and isolated.